

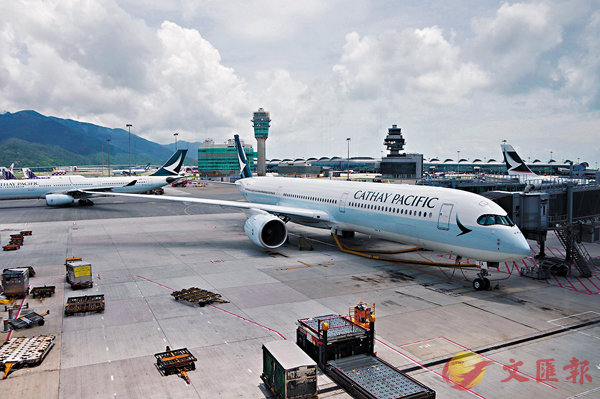
 ■早前國泰及港龍航空約940萬名乘客個人資料被不當取覽。 資料圖片
■Jeffrey Tse (ywc_jeffrey@hotmail.com)
原文
立法會於本月14日討論國泰及港龍航空約940萬名乘客個人資料被不當取覽一事,多名議員批評國泰隱瞞事件,並要求當局盡快修改私隱條例,加重罰則。
香港人素來注重保障私隱,隨�荇犮N和科技發展,隨�茩茪H資料的無形價值越來越高,企業、機構在獲取、使用客戶個人資料時外洩的風險也越來越高。
本港《個人資料(私隱)條例》已生效22年,條文明顯過時且阻嚇力不足,間接令私隱外洩事件頻生。政府有必要與時俱進修改法例,更切實有效保障市民私隱和利益。
在移動智能時代,個人資料日益成為極具價值的大數據資料。擁有大量客戶個人資料的航空、電訊和各類服務企業,自然成為黑客盜取個人資料以求不法利益的對象。私隱專員公署去年的工作報告顯示,2017年署方接獲106宗機構外洩個人資料事故的通報,較2016年上升近兩成。今年至今,除了國泰事件外,已先後有縱橫遊、大航假期、香港寬頻等企業的客戶資料被黑客盜取。類似事件頻繁發生,敲響個人資料保障的響亮警鐘。
但本港已行使22年的《個人資料(私隱)條例》,規管不嚴、罰則寬鬆,被譏為「無牙老虎」。對於機構洩露客戶資料,目前本港法例並無要求強制通報,只有相關指引給機構。
當然,私隱專員公署調查後覺得有必要,可對機構發出執行通知,不遵守執行通知屬刑事罪行,但最高罰款只是港幣5萬元及監禁兩年。如此輕微的罰則,明顯與個人資料外洩造成的損失不相稱。
2010年7月,八達通公司被揭發將197萬名「日日賞」客戶的資料售予6間公司,從中獲利4,400萬元,事後私隱專員公署裁定八達通公司違反私隱條例,但並無發出執行通知或作任何處分。事件不了了之。
《個人資料(私隱)條例》於1996年生效時,當時互聯網剛剛發軔,更無智能移動通訊,根本難以想像互聯網服務和電子支付服務有今天的普及。隨�茈禶~、機構近年收集個人資料的數量以幾何級數上升,洩漏事件一再發生,法例過時、監管嚴重不足的問題迅速惡化。因此,本港必須參考其他先進地區的做法,因應實際需要適時修法。
歐盟今年就通過了《通用數據保障條例》(GDPR),就外洩通報、資料轉移、加重罰則等諸多方面嚴格規管,任何在歐盟設立或目標受眾是歐盟公民的企業均受規管。一旦發生洩漏私隱事件,最高罰則是企業全球營業額的4%或2,000萬歐元,以較高者為準。
保障個人私隱,就是保障市民利益,市民對此有強烈訴求。期待政府聽到市民的呼聲,順應民意,盡快就修例提出建議,並諮詢公眾意見,堵塞法例漏洞,為市民的私隱安全把好法律關。
(標題為編輯所加)
(摘錄自香港文匯報社評 15-11-2018)
譯文
Lawmakers accused Cathay Pacific Airways of a cover-up as the Legislative Council (Legco) discussed the commercial flight giant's massive passenger data breach at a November 14 meeting. The data leak affected about 9.4 million Cathay Pacific and Cathay Dragon customers. During the meeting, legislators have also demanded the authorities to review the current privacy laws as soon as possible to introduce heavier penalties.
Privacy protection has always been paramount to the people of Hong Kong. However, as the value of personal data grows over time due to technological advancement, enterprises and institutions now face a greater risk of data leaks when obtaining and using the personal information of their customers.
Hong Kong's Personal Data (Privacy) Ordinance has been in force for 22 years. Its provisions are clearly outdated and insufficient as a deterrence, thus indirectly leading to the frequent data leak incidents. The government must keep pace with changing circumstances and make amendments on the ordinance, so as to protect the privacy and interests of the public more effectively.
In the era of mobile intelligence, personal data is becoming increasingly valuable as part of the big data.
The aviation, telecommunications and other tertiary sector industries that gather a large amount of customer data naturally became the target of hackers, who would steal personal information for illegal purposes.
According to the Office of the Privacy Commissioner for Personal Data (PCPD) Annual Report 2016-17, 106 data breach incidents were reported to the Office in 2017, which represented approximately a 20 per cent increase as compared with 2016.
Apart from Cathay Pacific, a number of companies including WWPKG, Big Line Holiday and Hong Kong Broadband have already fallen victim to customer data breach incidents so far in 2018. The frequent occurrence of data security incidents has sounded the alarm on privacy protection.
However, the 22-year-old Personal Data (Privacy) Ordinance has been reduced to a "toothless tiger", for its enforcement is ineffective and its penalties for contravention light.
Under the current laws of Hong Kong, only some guidelines on data breach handling are given, but there is no mandatory requirement for any organisation to file a notification to the PCPD in case of a data breach.
While the PCPD could issue an enforcement notice to the organisation involved after investigations were conducted, and that contravention of the notice is an offence, the maximum penalties are a mere fine of HK$50,000 and two years of imprisonment.
Such penalties can in no way be considered as commensurate, given the magnitude of the loss that is caused by a data breach.
For instance, Octopus Holdings Limited was found to have sold the personal data of 1.97 million cardholders under the "Octopus Rewards" programme in July 2010. The personal information was sold to six business partners of Octopus Holdings, and the company was able to amass HK$44 million from the deal.
Even though the PCPD found that Octopus Holdings violated the Ordinance, it did not issue an enforcement notice and no further action was taken.
When the Personal Data (Privacy) Ordinance was enacted back in 1996, the internet was just beginning to emerge, and there was no mobile communication. No one could have imagined the growth of internet services and the development of electronic payment.
As the volume of personal data collected by companies and organisations skyrockets, and that data leaks are becoming increasingly frequent, the problems of obsolete laws and ineffectual supervision would only get worse. Hong Kong must draw experience from others and review our current laws.
As an example, the European Union (EU) has just approved the General Data Protection Regulation (GDPR) this year. The law applies to all EU companies and those companies which offer goods or services to the citizens of EU, and imposes strict regulations on data transfers, breach notification mechanisms and penalties. Penalties for violating the GDPR could go up to ��20 million or 4 per cent annual global turnover, whichever is higher.
To protect personal privacy is to protect the interests of the public, of which there is a strong aspiration.
One hopes that the government will listen to the voice of the people and propose to review the Ordinance as soon as possible, so that the current loopholes in privacy protect could be rectified.
Exercise
1. 合規
2. 私隱專員
3. 透明度
4. 網絡攻擊
5. (條例)制定
Answer
1. compliance
2. the Privacy Commissioner
3. transparency
4. cyberattack
5. enactment